How to Structure User Permissions: The 3-Layer Rule
Most SaaS apps ship with role hierarchies no one asked for. Start with owner, member, viewer - add complexity only when real workflows demand it.
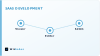
Most SaaS products ship with elaborate role hierarchies that no one asked for. Then they spend months undoing them when the first real customer workflow doesn't fit.
What actually decides your permission model is the smallest unit of work one person needs to do without involving someone else. If you can name that action and the two or three types of people who perform it, you have enough structure to launch.
What actually decides your permission model
Three structural choices lock in how permissions behave across your entire app.
Whether you separate data by workspace or share it across accounts. A workspace-per-customer model means one user cannot see another's records at all. That isolation is enforced at database architecture and tenant isolation level, not just in permission checks. A shared-data model puts everyone in one pool and relies on role-based access control to filter what each user sees.
Who assigns roles. Workspace owners controlling roles themselves means you need admin interfaces and invite flows. Assigning roles centrally gives you tighter control but slower onboarding.
How fine-grained permissions go. Coarse permissions are simple: admin, editor, viewer. Granular permissions let you control individual features or record types but require more UI and more logic to maintain. Start coarse. Add granularity only where friction proves it matters.
These three decisions shape every permission check you write. Change them later and you rewrite the access layer.
The questions to settle before adding roles
Start with who needs to see what.
List the actual people who will use your system and what they need to do inside it. A project management tool needs contractors who view tasks, managers who assign work, and admins who control billing. A healthcare platform needs patients who book appointments, clinicians who write notes, and practice owners who see revenue reports.
Decide whether people work alone or in groups. If your product serves individuals, role-based access control is enough. Teams sharing workspaces need tenant isolation so one company's data never leaks into another's.
Map permissions to features you are actually shipping. Do not design admin privileges for audit logs if you are not building audit logs yet. Your access control should match the scope of building your SaaS MVP, not the system you imagine in two years.
These three questions give you the permission structure you need at launch. Everything else can wait.
How to structure permissions at launch
Owner, member, and viewer.
Owner can change billing and delete the workspace. Members can create and edit. Viewers can see everything but change nothing.
That covers most SaaS apps at launch. Add a fourth level only when you have evidence that the three-level model is causing friction.
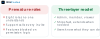
Role-based access control gets complex fast. Each new role multiplies the number of states your UI must handle. Add Manager and Admin and you now have five roles and dozens of permission combinations to test.
An alternative is workspace permissions tied to tenant isolation. Each user belongs to one workspace and sees only that workspace's data. No cross-workspace visibility. No global admin except at the platform level.
If different teams need different data visibility or compliance requires separation of duties, add the layer. Otherwise, wait until support requests tell you what's actually needed.
Most full-stack web development projects start with owner-member-viewer. They add roles later based on how customers actually use the product. Keeps the permission model tight. Keeps the codebase easier to test.
What to check before you ship
Run your permission model against real support tickets and onboarding calls before you lock it in. If your first three customers need the same workaround, the model is wrong.
Test the three scenarios that break most early access layers:
- Someone joins mid-project and needs partial access to old work
- A client wants to review without editing, or edit one thing without seeing everything else
- The person who set it up leaves, and no one else knows how it works
The goal is a structure you can extend when the actual edge case appears. Not the ones you imagined.
Most permission bugs surface in the first week of real use. Still explaining how roles work after three onboarding calls? Simplify it before you add more.
The permission model that survives is the one your team can describe in one sentence. One that lets you ship the feature what shapes a custom build without rewriting access logic every sprint.
How to tell your permission model is right
Run these checks before you commit the permission structure to production. A model that works on paper can still break when real users interact with it.
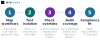
Your model is right when someone can complete their core task without hitting a permission wall or needing manual intervention. Support team fielding regular access requests means the role-based access control is too narrow or the defaults are wrong.
Watch for these signals:
- New users ask what permissions they need before they can start
- Admins grant exceptions more often than they enforce the default roles
- Cross-team workflows require coordinating workspace permissions across multiple accounts
A good permission model is invisible. Users finish their work and never think about access control at all.
Frequently asked questions
How do I know if I need role-based permissions at all?
If more than one person needs different levels of access to the same data, you need permissions. A solo product with one admin does not.
What happens to permissions when someone leaves the team?
Their account stays in the system with access revoked, so audit logs and ownership records remain intact. Delete the account only if you need to remove all trace of their activity.
Can I change someone's role without breaking things?
Yes, if your permission checks run at request time rather than being cached. Role changes take effect immediately and do not require the user to log out.
Should I let users create their own custom roles?
Not at launch. Custom roles add a second permission system on top of the first and make every feature harder to reason about. Wait until a client explicitly pays for that flexibility.
What if I get the structure wrong and need to change it later?
A migration script updates the database, and existing sessions stay valid as long as the underlying permission checks still work. The structure can change without losing data.
How do I test permissions without setting up dozens of test accounts?
Write unit tests that call your permission-check functions directly with different role inputs. You confirm the logic without clicking through the UI as each role.